 PrimetimeGeek independent technology journalism · relaunched 2026
How to back up your digital life so you can actually restore it
A second copy is only useful if you can find it, open it and recover from a lost device or compromised account. Here is a practical plan for people and small teams, including what cloud sync cannot do.
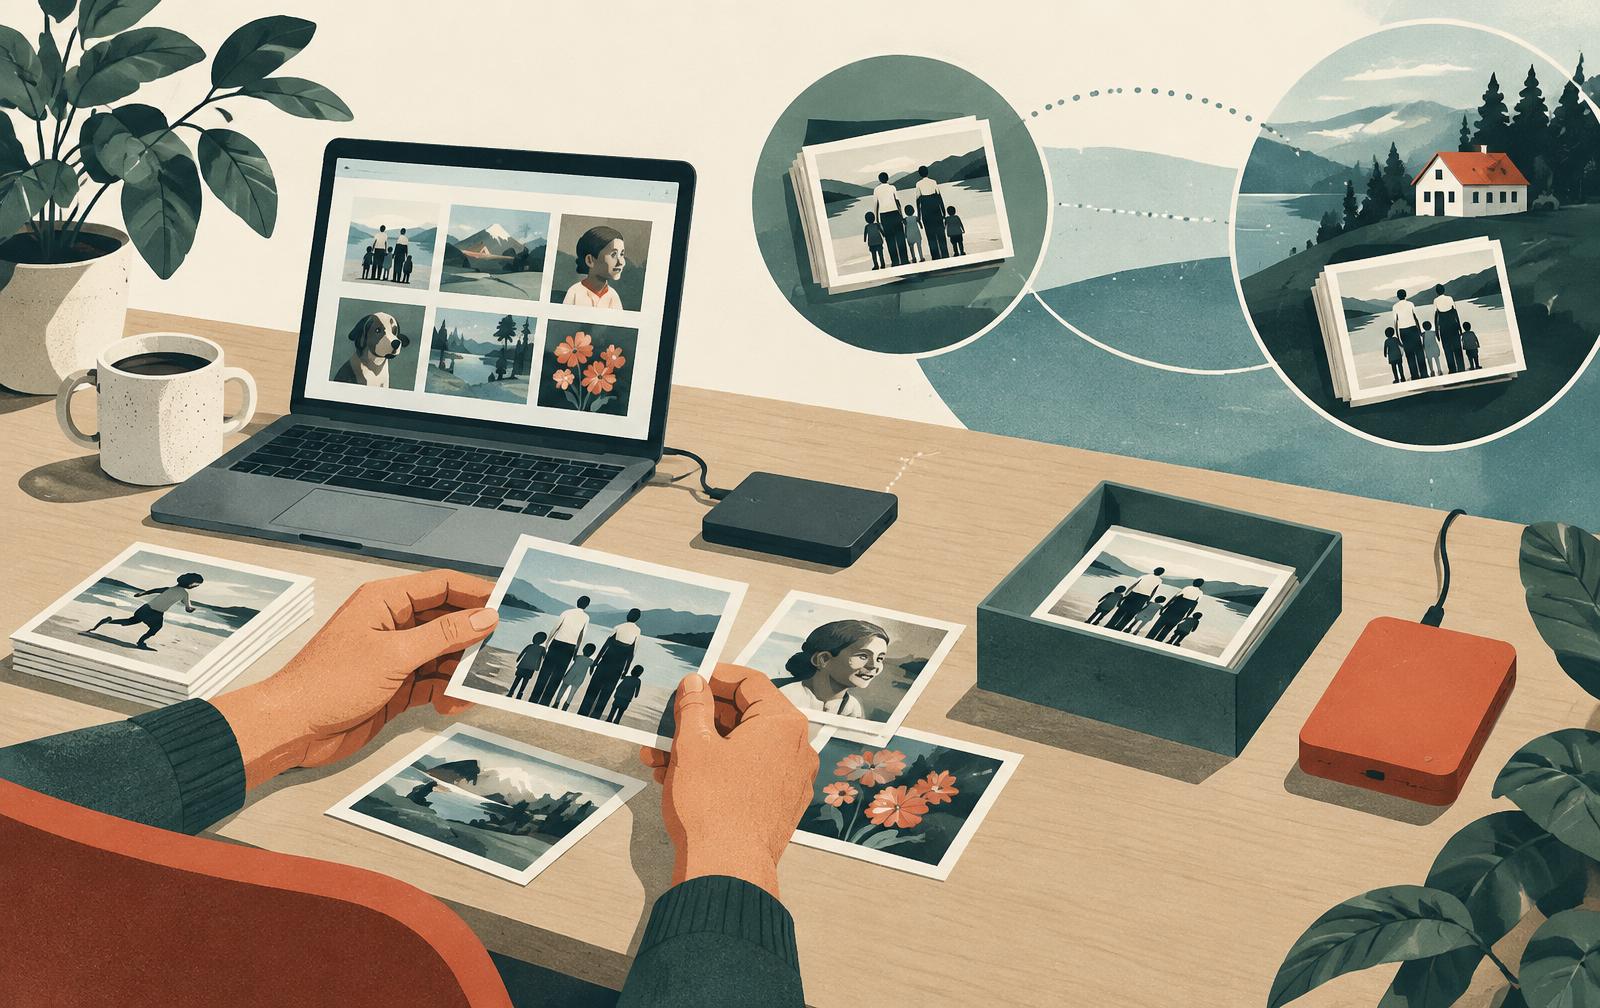
You can replace a phone. You cannot easily replace a decade of family photographs, the only copy of a manuscript, or the records a small business needs to reopen after an incident. Backups are often described as a storage purchase, but they are really a recovery process. The question is not “Do I have another copy?” It is “If this device or account disappears today, which files can I restore, from where, and how long will it take?”
This is a vendor-neutral guide for US readers. Federal preparedness and contingency-planning guidance supports making separate copies and testing recovery; the schedule and examples below are practical editorial recommendations, not a guarantee against every failure. Legal retention requirements, regulated data and complex business systems may need a tailored plan.
The short answer
Keep at least one current copy separate from your everyday device, and another copy that a stolen device, accidental deletion or compromised account cannot silently erase. Know which accounts and encryption keys unlock those copies. Restore a few real files on a regular schedule. If the files are critical to your livelihood, test recovery of the whole workflow, not just a sample document.
First, decide what would hurt to lose
Make a short inventory before choosing a tool. Include photos and videos, original project files, tax and financial records, notes, contacts, locally stored email, authenticator or recovery-code exports where supported, and the settings needed to reconstruct a device. Check phones, laptops, external drives and the accounts family members use. A folder that looks synchronized may omit material stored only in an application's local library.
Sort by recovery priority. Irreplaceable means no source can recreate it. Time-critical means you need it quickly even if another copy exists. Re-downloadable means installation files, purchased media or public documents you can obtain again, though licenses and access may complicate that assumption. A one-page inventory with the location, owner, backup destination and last restore test is more useful than a vague promise to save everything.
For a small team, add shared drives, billing records, customer deliverables, domain and account recovery details, and any data held by a service you might lose access to. Someone must own each item. “It's in the cloud” is a location, not a recovery plan.
Understand the difference between sync, backup and archive
Synchronization keeps a working set of files similar across devices. It is convenient, but a deletion, corruption or unauthorized change may propagate to every synchronized device. Some services provide file history and trash recovery, but retention periods and coverage vary. Verify exactly which folders, file types and previous versions are recoverable, and for how long.
A backup preserves a separate recoverable copy or sequence of versions. Versioning matters because you might discover a damaged file weeks after the damage occurred. An archive is for long-term retention of material you rarely change; it may require different formats, labeling and periodic checks. One service can offer more than one of these features, but its marketing label is not proof that all three are configured for your data.
Build a failure-resistant arrangement
A useful starting pattern is the “3-2-1” rule of thumb: three copies of important data, on two kinds of storage or independently managed locations, with one copy off-site. It is a heuristic, not a magic number or a compliance standard. The failure modes matter more than counting boxes. Two drives left beside one laptop can be lost to the same theft or fire; two cloud folders under the same compromised login may fail together.
For a household, that could mean the working files on a computer, an automatically updated external drive disconnected when the job finishes, and a separate remote backup with version history. A person with only a phone may instead use a cloud backup plus a periodic export of irreplaceable photos and documents to a drive kept elsewhere. Check that the export produces files you can actually open on another device.
For a small organization, pair routine backups with an off-site or logically isolated copy whose deletion controls are separate from ordinary user accounts. A disconnected drive or appropriately configured immutable retention can limit damage from ransomware, but neither helps if the backup is stale, incomplete or inaccessible when needed. CISA's ransomware guidance emphasizes protecting and testing backups as part of incident preparation, not as a substitute for prevention.
A seven-step setup you can finish
1. Choose the recovery target. Pick the files and accounts you need to recover first, and decide how much recent work you can afford to lose. A daily backup can still lose up to a day's changes.
2. Choose two independent destinations. Avoid one login, one physical location and one payment method as single points of failure wherever practical. Record who controls each destination.
3. Automate the frequent copy. A backup that relies entirely on remembering a weekly task tends to drift. Check what it includes and whether it runs when the device is asleep or away from home.
4. Add a separated copy. Disconnect a local drive after the backup, or use an off-site destination with version retention and protections against account-wide deletion. Protect backup credentials separately from the account they are meant to rescue.
5. Protect access without creating a lockout. Encrypt sensitive backups, use strong authentication for backup accounts and keep recovery keys in a safe place a trusted person can reach if necessary. Losing the only decryption key can be as final as losing the files.
6. Run a restore drill. From a different device or account session, recover a photo, a document with an older version and a complete folder. Open the files, check dates and names, and note how long the process took. Do not overwrite the only working originals during a test.
7. Put a date on the next test. Monthly checks are sensible for actively changing personal files; higher-stakes systems may need more frequent verification and periodic full recovery exercises. Revisit the plan whenever you change devices, accounts or storage providers.
What a restore drill reveals
A green status light may only mean a job completed. It does not prove all intended folders were included, the encryption key is available, a previous version survives, or the download is fast enough to meet your deadline. Try the recovery path on a spare or temporary device rather than browsing backup contents in the same app that created them.
If restoration fails, write down the specific reason: missing folder, expired version history, forgotten password, unavailable recovery email, unsupported file format, slow connection or a backup that stopped running. Fix that failure and retest. Small teams should also rehearse who authorizes a restore, who can access keys if the usual administrator is unavailable, and when to isolate a compromised system before bringing data back.
Special cases people overlook
- Photos and messages on phones. Confirm whether “backup” includes full-resolution originals, messages, app data and locally stored files. Different apps may have separate backup settings.
- Shared or departed-user accounts. Exporting a shared folder is not the same as preserving its permissions and ownership. Test the handoff before an employee or account leaves.
- Subscriptions and hosted tools. Your service provider may keep its own disaster-recovery copies, but those may not let you undo your own deletion or export your data after losing account access. Read the export and retention terms.
- Ransomware. Do not reconnect a clean backup to an infected machine just to see whether it works. Restore only after the environment is contained and trustworthy; an incident-response professional may be appropriate.
- Physical disasters. Off-site copies protect against a local event, but recovery also needs a working device, power, connectivity and a way to reach your credentials.
What the evidence supports — and what it cannot promise
NIST's contingency-planning guidance treats backups, alternate storage and testing as parts of a broader recovery program. CISA's ransomware guidance recommends maintaining backups and verifying their integrity. These are sound design principles, not a controlled comparison proving that one consumer storage product, exact backup frequency or “3-2-1” configuration will work best for everyone. The appropriate plan depends on what you store, how often it changes, the threats you face and the cost of downtime.
We cannot inspect your backup settings or verify a provider's current retention policy from this guide. Service interfaces, storage limits, export formats and recovery rules can change. Check the current documentation for each service you rely on and make your own restore test the deciding evidence.
The practical conclusion
Start with the irreplaceable files, automate a separate copy, keep another beyond the reach of the same accident, and schedule a restore test. The test is where a backup stops being a comforting assumption and becomes a plan you can trust. If the drill fails, that is useful information while your original device still works.